How to extend a private OVHcloud network across Public Cloud regions
Learn how to configure a multi-region OVHcloud private network, manage VLANs and IP pools to prevent conflicts, and integrate with other OVHcloud products
Objective
The objective of this guide is to help OVHcloud users configure and extend a private network across multiple Public Cloud regions, while avoiding IP conflicts and ensuring network stability. It covers best practices for:
- Assigning separate IP pools per region.
- Managing VLANs across regions or other OVHcloud products.
- Using DHCP as a service for additional infrastructure, such as Bare Metal servers.
- Providing step-by-step instructions using the OVHcloud Console, Horizon, Terraform, and OpenStack CLI.
By following this guide, users will be able to deploy a secure and reliable multi-region private network with OVHcloud.
Background and Solution Overview
Challenges
When extending a private network across multiple OVHcloud Public Cloud regions or connecting it to other OVHcloud products through a vRack, a major challenge arises from the way IP addressing is handled.
Public Cloud instances automatically receive their private IP addresses via OpenStack DHCP or cloud-init, and this mechanism cannot be disabled. At the same time, all private networks using the same VLAN inside a vRack must share a common address space. This means that, without proper planning, the same VLAN can end up assigning overlapping or identical IP addresses across regions or between different OVHcloud services.
To illustrate this issue, the following diagram shows an example of what must be avoided:
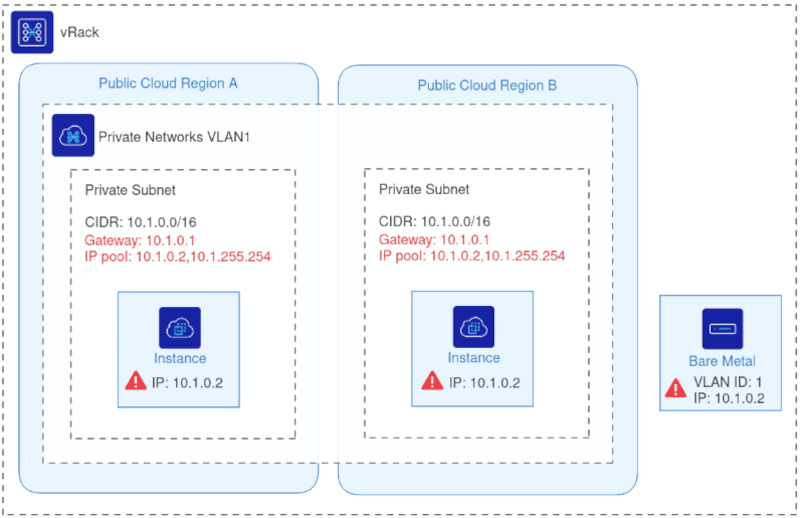
In this example, two Public Cloud instances in different regions and one Bare Metal server all share the same VLAN ID and have been assigned the same IP address.
When multiple machines share the same IP on the same VLAN, the network becomes unstable. Packets cannot reliably determine which machine they should reach. For example, any traffic sent to 10.1.0.2 may land on an unpredictable host, resulting in inconsistent connectivity, routing errors, and service disruption.
This problem becomes more severe as environments scale across multiple regions or products. Therefore, a structured approach to IP allocation such as dividing the subnet into dedicated per-region pools is essential to maintaining a stable, predictable and conflict-free vRack network.
Solution Overview
To prevent IP conflicts and ensure stable communication across a stretched vRack network, each Public Cloud region must use a dedicated IP pool within the same private subnet. By segmenting the subnet into non-overlapping allocation ranges, OVHcloud ensures that OpenStack DHCP services in different regions never assign duplicate IP addresses even when all networks share the same VLAN ID.
The diagram below illustrates the corrected configuration:
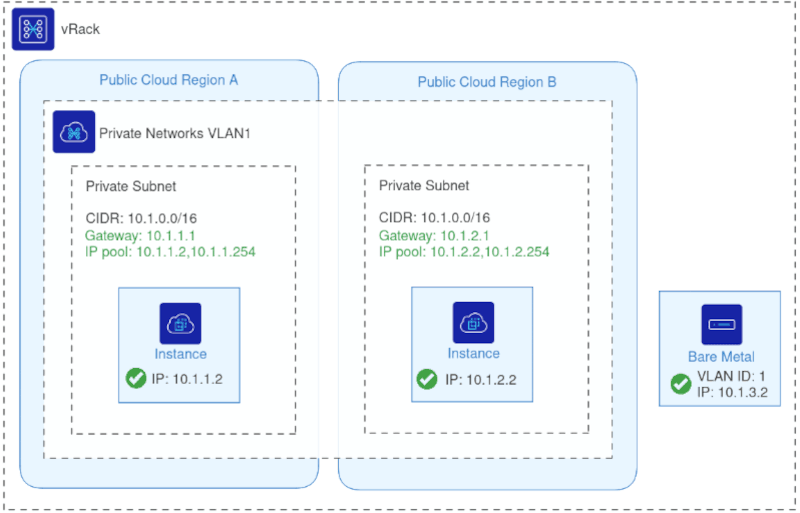
Each region uses the same VLAN ID but draws IPs from a distinct allocation pool within the shared subnet, eliminating any risk of overlap.
With this approach:
- All regions remain part of the same L2 private network through the vRack.
- DHCP continues to function normally in each region, as OpenStack assigns IPs only from its designated pool.
- Additional OVHcloud products (such as Bare Metal, Dedicated Servers, or Private Cloud) can join the same VLAN without creating address conflicts.
- Multi-region workloads, migrations, and hybrid deployments operate reliably on a unified private network.
This solution preserves the flexibility of a single stretched VLAN while enforcing predictable, conflict-free IP management. This guide explains how to configure this setup using the OVHcloud Console, Horizon, Terraform, or OpenStack CLI.
Use case examples
Here are some practical scenarios where extending an OVHcloud private network across regions or integrating with other OVHcloud products can solve real-world challenges.
- Database on Bare Metal & Application on Public Cloud: Connect a Bare Metal database server with applications running in Public Cloud regions using the same VLAN without IP conflicts.
- DHCP as a Service for Bare Metal Servers: Assign IPs from Public Cloud networks to Bare Metal servers via DHCP for seamless integration.
- Migration Between Public Cloud Regions: Move workloads from one region to another while keeping the private network consistent and avoiding IP conflicts.
- Multi-Region Services: Run distributed services across multiple Public Cloud regions with a unified private network for secure communication.
- Integration with Other OVHcloud Products: Connect Public Cloud instances with Private Cloud, Dedicated Servers, or other OVHcloud services through vRack.
Requirements
- A Public Cloud project in your OVHcloud account
- Basic networking knowledge
- Access to the Horizon interface
OVHcloud Console Access
Projects:
- Direct link:
- Navigation path:
Public Cloud> Select your project
vRack:
- Direct link:
- Navigation path:
Bare Metal Cloud>Network>vRack
Instructions
This section provides step-by-step instructions to configure a private network stretched across multiple OVHcloud Public Cloud regions. You can use the OVHcloud Console & Horizon, Terraform, or OpenStack CLI.
Configuration for Public Cloud
Add the Public Cloud project to a vRack. In the OVHcloud Console, open Bare Metal Cloud, click vRack under Network in the left-hand menu, then click the name of your vRack. In the Attached services tab, check that your Public Cloud project is listed. If it is not, click Attach a service and attach it (see Step 1 of the vRack guide).
1. Create private networks in each region
Create a private network in each desired region using the same VLAN ID.
In your Public Cloud project, click Private Network under Network in the left-hand menu, then Create a Private Network. Tick Set VLAN ID and enter the same VLAN ID in each region (see the vRack guide).
Note: At this stage, using the same VLAN ID across regions without separate IP pools is exactly what must be avoided.
2. Configure subnets and IP pools
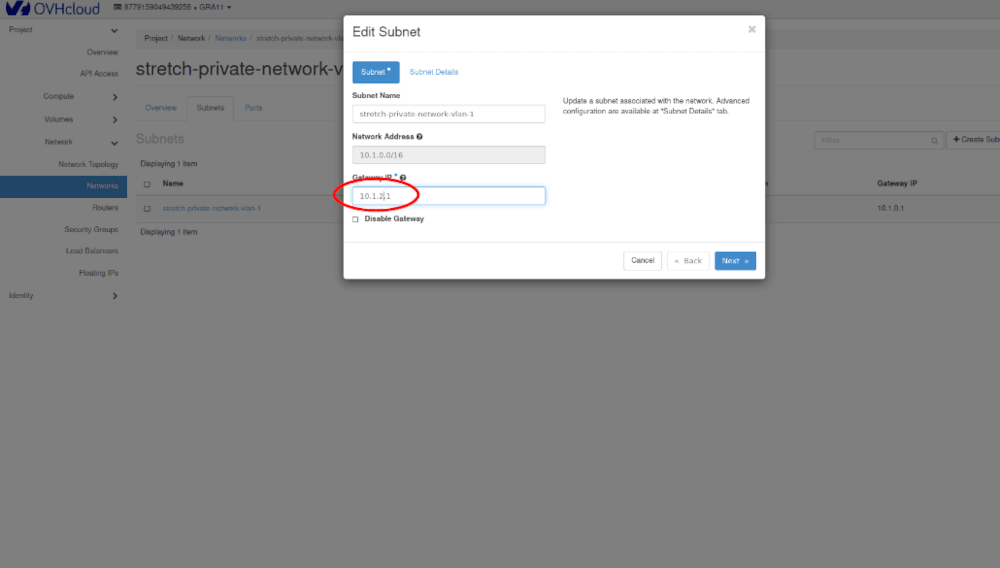
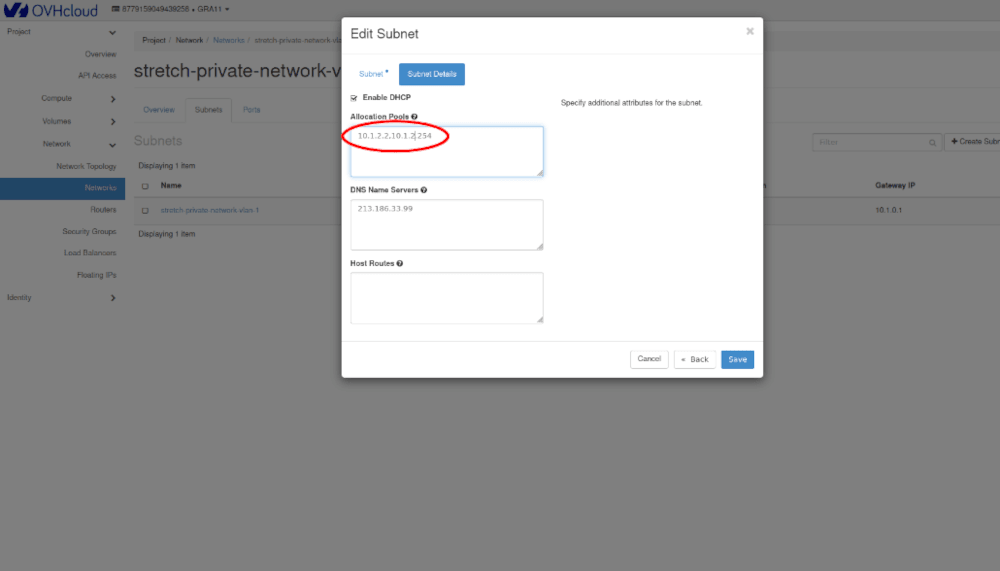
Edit each subnet in Horizon, configure the gateway reserved IP and the IP pool.
- First region:
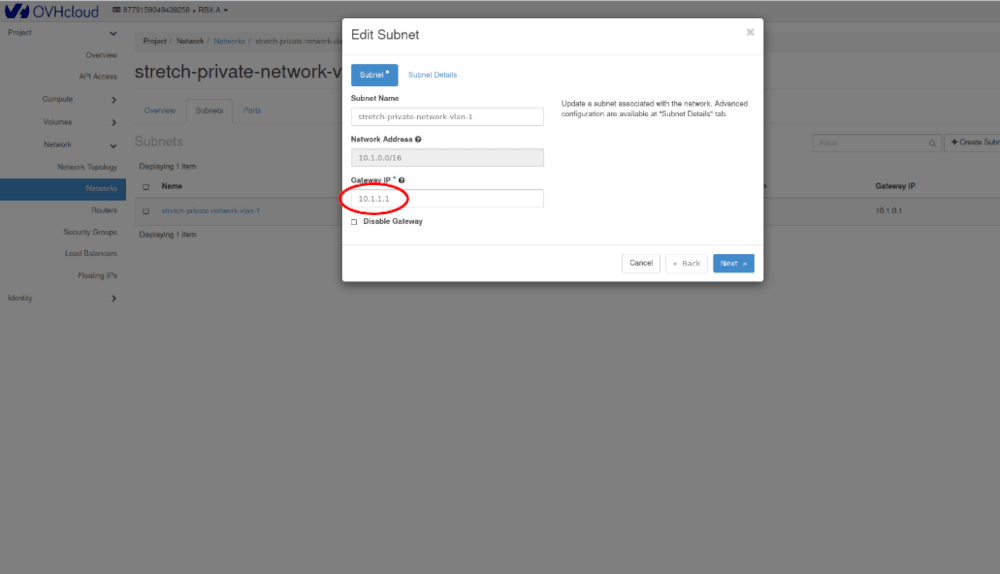
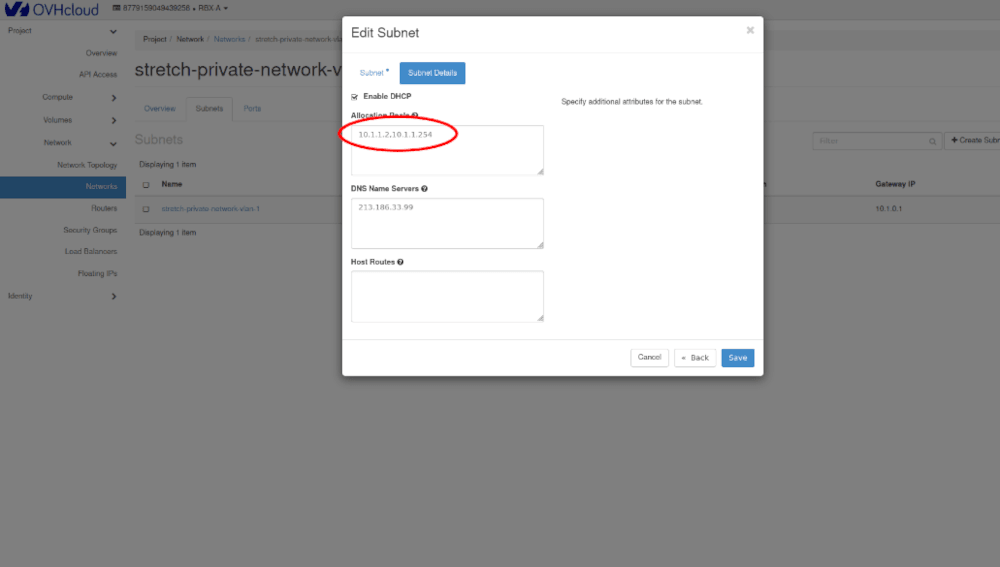
- Second region:
3. Refresh network status
Go back to the OVHcloud Console and refresh the Private Network page (tab Regions (vRack)).
You should now see a single VLAN stretched across multiple regions, each with its own IP pool.
DHCP for Bare Metal Servers (DHCP as a Service)
This section explains how to provide Public Cloud DHCP IP addresses to Bare Metal servers by integrating them into a stretched private network.
The Public Cloud project and Bare Metal server must be added to the same vRack. In the Attached services tab of your vRack (Bare Metal Cloud > Network > vRack), check that both the Public Cloud project and the Bare Metal server are listed; attach them with Attach a service if needed.
1. Create a Public Cloud private network
In your Public Cloud project, click Private Network under Network in the left-hand menu, then Create a Private Network. Tick Set VLAN ID to choose the VLAN ID.
Note: Use the same VLAN ID that will be used for the Bare Metal server.
2. Obtain the MAC address of the Bare Metal server’s private interface.
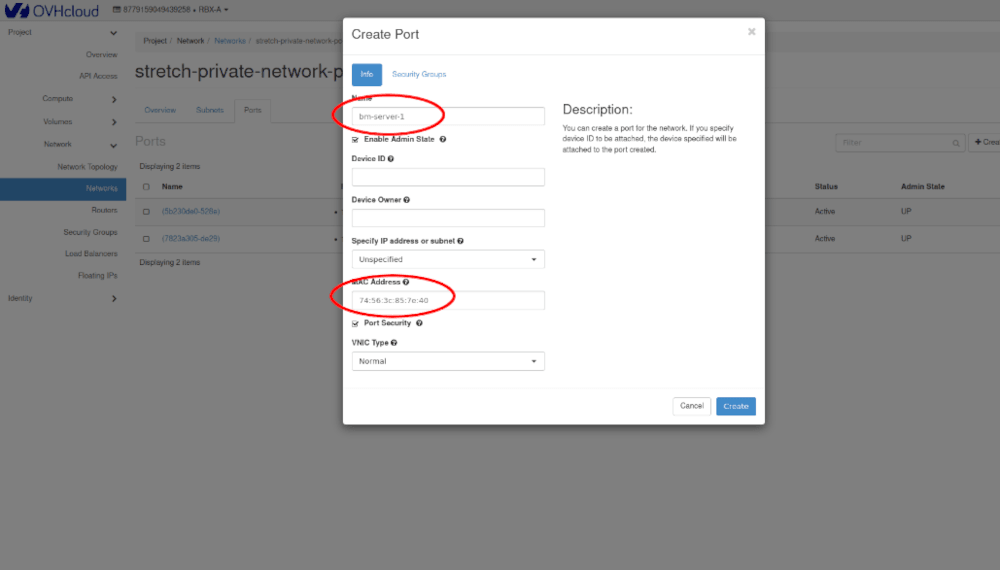
In the OVHcloud Console, open Bare Metal Cloud > Dedicated servers, click the name of your server, then open the Connectivity tab. Note the MAC address shown in the Private interface (vRack) section.
3. Create a virtual port on the Public Cloud private network using the MAC address of the Bare Metal server.
4. Install an operating system on the Bare Metal server (e.g., Ubuntu 24.04).
Note: Post-installation scripts may need to be updated with the correct MAC address and VLAN ID.
Notes / Best Practices
- Verify the VLAN ID matches between the Public Cloud network and Bare Metal server.
- Confirm the Bare Metal server receives an IP from the Public Cloud DHCP service after installation.
- Each server should use a dedicated IP allocation pool to avoid conflicts.
Go further
Join our community of users.